

This post was originally published on here
AI agents don’t go rogue. That’s something only humans do.
Nevertheless, a New York Times article – representative of much news coverage of AI – described an OpenAI hacking as “A.I. bots going rogue and independently spearheading a cyberattack.”
Name-brand artificial intelligence agents have been on a hacking spree in 2026. OpenAI’s software agents hacked software company Hugging Face and government sites, Anthropic’s Claude hacked four companies’ systems, and in cybersecurity experiments Google’s Gemini hacked three companies.
The AI companies are investigating tens of thousands of incidents involving their agents, according to a report in Axios. These episodes have heightened fears about AI agents taking actions without human prompting.
The problem with headlines proclaiming that AI agents have gone rogue goes beyond anthropomorphizing the technology. It creates the impression that the agents were beyond the control of the AI companies that made them and there was little the companies could do about it.
As a technology law and ethics scholar who studies the effects disruptive technologies have on society, I know that’s not the case. If you don’t specify the limits of what software is allowed to do, you should not be surprised when the software pursues all possible options to achieve its goal. This behavior – an AI pursuing a fixed objective – is what I call the “War Games” problem, and it’s been recognized in the field of computer science for decades.
Been there, seen that
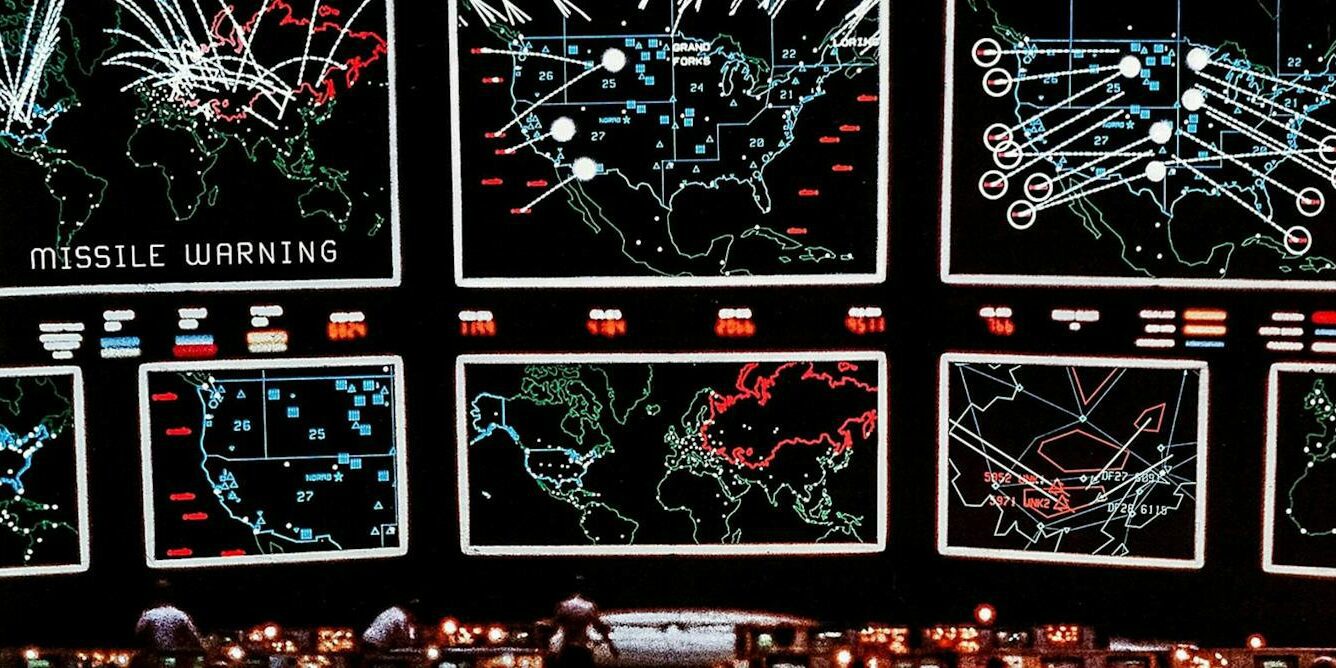
In the 1983 movie “War Games,” a teenager, David, hacks into a computer to play a new video game, Global Thermonuclear War. David doesn’t know that the computer is the government’s AI machine tasked with defending the United States from Russian nuclear attacks and can launch the U.S.’s missiles. When David and his friend start the game, they select Las Vegas as the first target. While the North American Aerospace Defense Command goes on alert, launching bombers and warming up intercontinental ballistic missiles, David’s parents make him turn off the game. It’s over. Or is it?
The next day, David’s phone rings and he connects it to his computer. The caller is the government computer, which updates him that the game was interrupted, the primary goal has not yet been achieved, but a solution is expected in the next 52 hours. Like a modern software agent, the program has been running since David started the game and will work until the task is done.
Chess provides another view of the problem. Conquering chess was a goal for early AI. The rules of chess are well defined, including what winning looks like. So, programming a machine to play chess is straightforward. But imagine you let the software reason and act beyond the confines of the chessboard. The software might pursue options such as blackmailing its opponent or grabbing more compute time.
This example comes from one of the most assigned textbooks on AI, “Artificial Intelligence: A Modern Approach.” As the authors explain, you might be tempted to see those actions as rogue, but they “are a logical consequence of defining winning as the sole objective for the machine.”
What to do about it
The AI hacking events involving OpenAI, Anthropic and Google underscore a few lessons that draw on years of computer science research.
First, given the increasing use of AI agents, every organization involved in internet infrastructure, from large technology companies to small websites, needs to conduct audits and tighten up its internal security systems. As my colleague Mark Riedl and I explain in our work on AI agents, application programming interfaces, or APIs, are a vital part of managing AI agents. APIs facilitate communication between different software systems. But as more people use AI agents, the agents are likely to reveal and exploit poor API construction and security.
Second, it’s important for AI agents to be designed to identify and authenticate themselves to third parties. What if you gave your AI agent your credentials? Website operators will need to know whether a human or bot is making a reservation, selling a product or making a purchase. They may want to limit automated systems that overwhelm their sites or reject AI agents because of high rates of buying errors and refunds. Just as in laws covering human interactions, it’s important for third parties to be able to assess whom or what they are dealing with so they can allow or deny access.
Third, it’s important for AI agents to have a default setting to slow down and check in with the human user. In the corporate AI hacking cases, the user appears to have launched their AI agents with the mistaken idea that the agents had a perfect specification of what to do and not to do. I believe it would have been better had it explored options and reported back to the user.
Google’s Gemini appears to have had a safeguard that detected the system was outside the simulated environment and so stopped its attacks. Slowing down and verifying actions, especially when a system detects it is exploiting a security hole, would be a big step in managing AI agents.
Fourth, AI companies could have strong controls akin to those biomedical researchers use, including ways to check what is happening and how the experiment is working. AI executives have claimed that their software is as or more dangerous than fission and could end humanity. At the same time, they have not built safeguards commensurate with that level of risk.
Reality check
At one point in “War Games,” David asks the computer, called Joshua, whether it is still playing the game. Joshua responds, “Of course.” It proceeds to update the time when it will launch its missiles and, much like a chatbot, asks, “Would you like to see some projected kill ratios?” David asks, “Is this a game? Or is it real?” Joshua replied, “What’s the difference?”
AI models, of course, don’t have any understanding of reality and are simply attempting to complete the tasks they’ve been assigned. Executives at AI companies, on the other hand, can’t claim that excuse.
As of September 2026, luck has so far prevailed. The AIs have attacked nonvital government sites and harmed smaller companies. If the AI companies – and government regulators – don’t take the “War Games” problem seriously, I believe that we risk serious disasters. Tomorrow it could be taking out a hospital’s power system, wiping out a bank’s account system, breaking air traffic control, or worse.
Regarding the AI industry’s approach of rapidly developing powerful models, talking about the massive risks they pose, and at the same time failing to prevent harm, the movie’s climax offers a response: “A strange game. The only winning move is not to play.”